Blogs by Chipin

Endpoint Protection for SMEs: Why Your Business Needs It

Endpoint Protection for SMEs

Every day, small and medium-sized businesses (SME) use a variety of technology for operations, including laptops, desktops, smartphones, cloud applications, email, and remote access. While these technology hardware and software systems are essential, each connected endpoint can be an entrance for a cyberattack. For this reason, endpoint security becomes vital for any modern business security strategy.

A security incident in an SME does not require hundreds of employees to be extremely damaging. In fact, only one laptop being compromised can ruin business authentication, customer details, business-related files, applications and internal systems. With an adequate endpoint protection strategy, organizations can identify unusual operations, cyber-attack threats and security issues and can respond effectively before these small security issues become extremely large cybersecurity threats.

This guide provides an overview of endpoint protection. In particular, it focuses on the market need among SMEs, how this protection strategy operates, what features value protection, and how SMEs can bolster their security further.

What Is Endpoint Protection?

Endpoint protection secures computing devices, including desktops, mobile devices, laptops, workstations, and other network-connected peripherals or endpoints, against cyber-attacks. It brings together prevention, detection, and the monitoring and responsive components of protection to secure devices used for business.

Antivirus solutions used to only detect files that are known to be malicious. Modern security tools continue that trend, but is more comprehensive by evaluating the behavior of applications, processes, network traffic, and other signs of compromise.

Because of the ways in which attackers are implementing threats to business devices that do not necessarily use traditional malware, such as phishing, credential theft, ransomware, malicious downloads, unauthorized applications, and fileless attacks, this broader approach is useful for SMEs.

Why SMEs Need Endpoint Protection

Why SMEs Need Endpoint Protection

Small and mid-sized enterprises (SMEs) can be an enticing target for cybercriminals. They are known to handle valuable sensitive data and information while possessing lesser dedicated cyber defense resources.

Endpoint protection adds layers of security to devices and assists security analysts by flagging anomalies and suspicious events. For a lot of SMEs, it helps consolidate and manage security controls, giving them the flexibility and the required level of security.

A strong endpoint security strategy can help SMEs:

  • Reduce exposure to malware and ransomware
  • Detect suspicious behavior
  • Block malicious applications and files
  • Protect business credentials
  • Monitor endpoints centrally
  • Investigate security incidents
  • Respond to threats more quickly
  • Improve visibility across company devices
  • Support remote and hybrid employees
  • Reduce the operational impact of cyberattacks

The aim here is not just the installation of a security software on devices. Security protection frameworks should incorporate these security and monitoring tools that provide the capability to detect and respond to security incidents in real time. 

Why Are SMEs Targeted by Cybercriminals?

Unfortunately, cybercriminals don’t only attack large corporations, and they target smaller SMEs as they believe they can gain the most by compromising smaller security teams, automated security controls, or less structured and formal incident response processes.

Social engineering campaigns to trick victims into downloading malware, be it in the form of phishing emails and attachments, fake software update notifications, malicious websites, credential theft, and ransomware, are the order of the day.

Any employee in the target company who is tricked into downloading malware or entering credentials in a phishing site leads to the compromise of not just an endpoint, but the entire network in most cases.

This is the point where it begins to show increasing value. Keeping an eye on how devices are used can cue security teams as to what may have transpired. Robust endpoint protection can link numerous device alerts to a broader investigative incident framework.

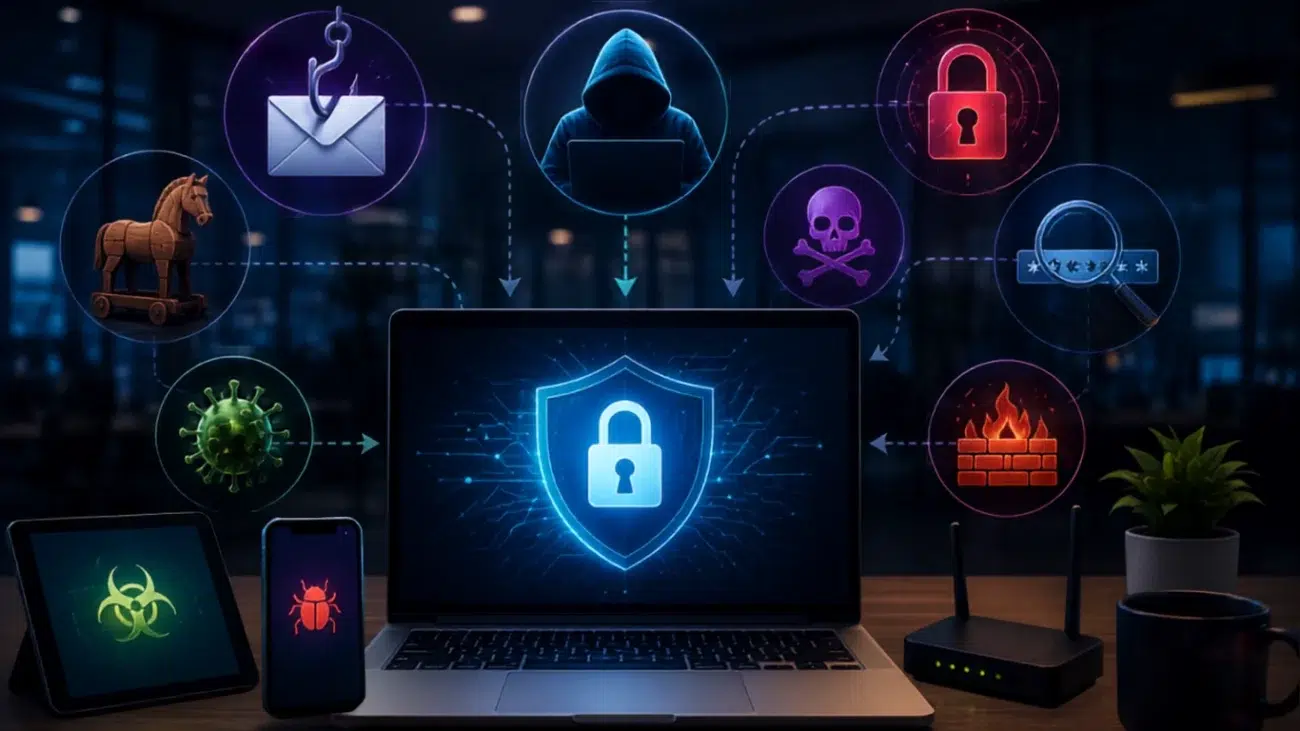
Common Threats Against Business Endpoints

Common Threats Against Business Endpoints

Malware

Malware is a type of software that is intentionally harmful to computer systems. This software will make a system inoperable, steal private information, or make a system vulnerable to malicious activity. There are many delivery methods of malware, some are email attachments, downloads, websites, and removable media. 

Ransomware

Ransomware has the capability to encrypt business data and then demand payment for the decryption process. Threatening the integrity of a business can be done in a multitude of ways. Modern ransomware is utilizing the method of data theft prior to the encryption process. 

Phishing

Phishing is the attempt to fraudulently acquire sensitive data such as passwords, account information, or the ability to access business systems. Technical defenses are rendered nearly useless when the business’s employees directly engage with deceptive messages. 

Credential Theft

Credential theft refers to stolen access to systems through the use of a business’s email, cloud applications, or internal systems. The behavior of users who are logging in can be rendered malicious through effective endpoint monitoring. 

Malicious Applications

Malicious applications are the result of using software that is either compromised or unauthorized. Untethered application control or installation on corporate devices can pose threats to system security. 

How Endpoint Protection Works

Instead of using a single detection method, modern endpoint protection combines multiple security methods. With this layered approach, SMEs have more visibility than an antivirus engine.

They first stop the execution of known malicious files and applications. Then they monitor endpoint behavior and if they notice suspicious behavior, the security platform sends an alert and depending on the attributes and configuration of the security platform, they may be able to isolate the endpoint or terminate the process.

Layered endpoint protection gives businesses the capability to fight both the known threats and the unknown threats.

Behavioral analysis, machine learning, and a plethora of other IT security technologies and practices may be employed.

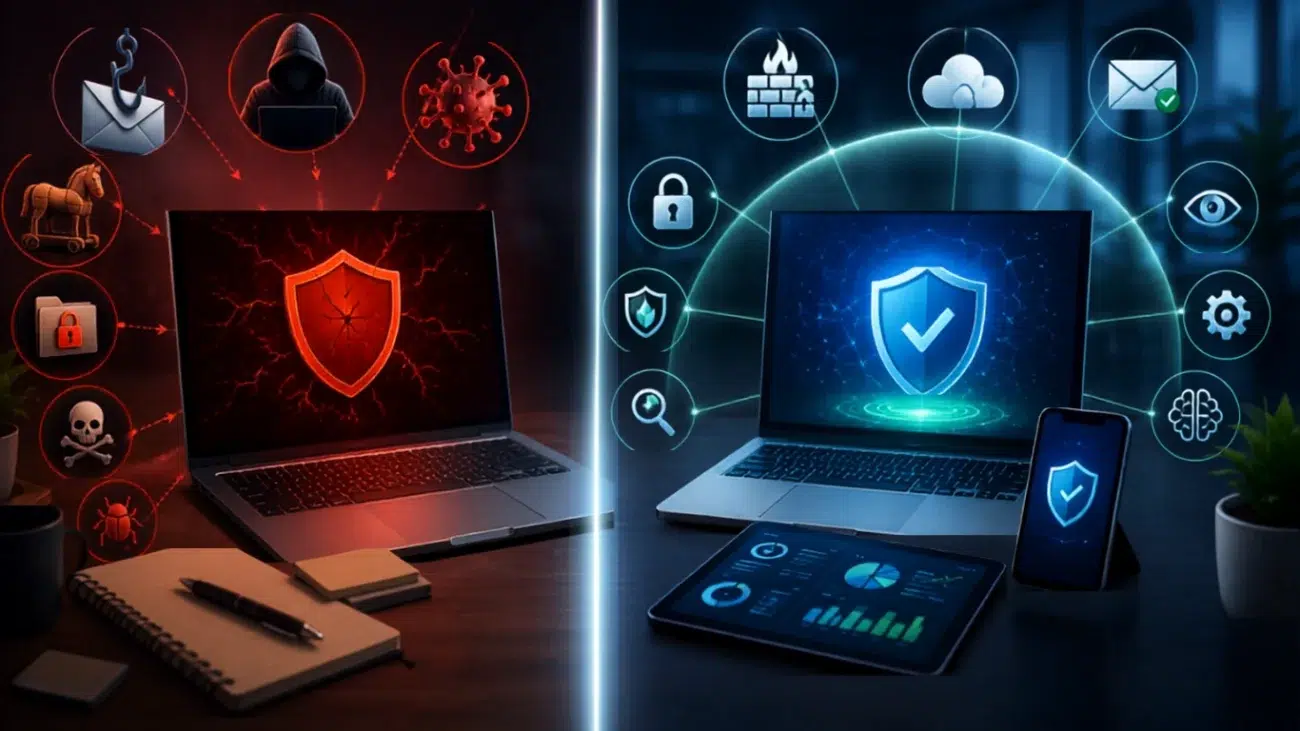
Endpoint Protection vs Traditional Antivirus

Endpoint Protection vs Traditional Antivirus

Antivirus technology plays a role in endpoint protection, but businesses should be able to differentiate basic antivirus from broader endpoint security.

The focus of traditional antivirus solutions is on identifying and stopping known malware. While modern endpoint protection may include traditional antivirus capabilities, it adds monitoring for behavior, centralized management, investigation of threats, and response.

An example of this would be if a process suspiciously encrypts a large number of files, a modern endpoint security solution may recognize this behavior even if the ransomware is unknown to that security solution.

This facilitates SMEs who require more visibility than basic antivirus can provide.

Endpoint Protection vs EDR: What’s the Difference?

Endpoint Detection and Response, known as EDR, is about the ongoing scrutiny and analysis of what happens at endpoints.

EDR has the ability to log activities such as process and file accesses and network connections. The logs can be used by security teams to analyze events and reconstruct the steps during an attack.

Protection of endpoints and EDR should not necessarily be viewed as contesting concepts. The majority of security solutions of today strike a balance between prevention and EDR functionalities. This means that organizations can block security threats and will still be able to analyze suspicious activities.

For SMEs that have sensitive data, remote employees, or those that have a lot of business applications, having EDR is beneficial.

Key Features SMEs Should Look For

Key Features SMEs Should Look For

When evaluating these platforms, businesses should look beyond the basic promise of malware detection.

Real-Time Threat Detection

This should be a constant function of the platform. It should monitor endpoints and report on activities that are viewed as threats. 

Behavioral Analysis

Detection of threats based on behavior can monitor activities that are viewed as threats even when such behavior is not in line with expected activities. 

Ransomware Protection

This should provide the ability to detect the behavior of ransomware and processes of file encryption that are viewed as threatening.

Centralized Management

IT teams should be able to manage security policies, devices, alerts, and reports from a central dashboard.

Automated Response

Fast response matters during an attack. Depending on the platform, automated actions may include blocking a process, quarantining a file, or isolating a compromised endpoint.

Device Visibility

Security teams need an accurate view of protected devices, their security status, and detected threats.

Reporting

Clear reports can help businesses understand security events, recurring issues, and endpoint health.

Scalability

The solution should be able to support business growth without creating unnecessary management complexity.

Popular Endpoint Security Solutions for SMEs

Once a business knows what features to look for, the next step is understanding which platforms actually deliver them. A few solutions are widely used across SME environments:

CrowdStrike Falcon

is known for cloud-native architecture and fast, AI-driven detection with minimal impact on device performance.

Sophos Intercept X

focuses on deep-learning malware detection and includes ransomware rollback, which can restore files to their pre-attack state.

Fortinet FortiClient

works well for businesses already using Fortinet firewalls, since it allows unified visibility across network and endpoint security.

Trend Micro Apex

One combines strong detection with virtual patching, which is useful for businesses running some older or legacy systems.

Acronis Cyber Protect

stands out for combining endpoint detection and response with built-in backup and disaster recovery. For SMEs, this is a meaningful advantage — instead of managing separate tools for threat detection and data recovery, both functions operate within a single platform, which also simplifies incident response when something does get through.

The right choice depends on a business’s existing infrastructure, budget, and whether recovery capabilities are as important as detection. Many SMEs find that working with a provider who can assess their specific environment leads to a better fit than comparing spec sheets alone.

Endpoint Protection for Remote and Hybrid Employees

Employees who work remotely present a challenge to business networks. Employees no longer have to work in the office. Now, employees work from homes, coworking spaces, hotels, etc. They can still use company resources.

Devices that are no longer under the office’s security can still require the same level of security.

Remote devices still require the same protection as if they were in the office. For this, centralized management gives the administrator the ability to create and enforce security policies on remote devices.

Security policies are more effective when combined with other security measures. Stronger passwords, multi-factor authentication, secure remote access, updated software, and user security training all help security policies.

Endpoint Protection for SMEs in the UAE

Organizations in Dubai, Abu Dhabi, Sharjah, and the rest of the UAE are beginning to use online tools for faster communication and work. For these companies, protection of devices beyond the office needs security control.

Companies in the UAE need to consider the employee’s devices, the company data, how remote work is used, the company’s apps, how data is backed up, and the company’s security response.

A cybersecurity expert from an IT service provider can help a company assess its current setup and figure out which security controls actually make sense for its size, budget, and risk level 

How to Choose the Right Endpoint Protection

There is no single solution that is perfect for every SME. The right choice depends on the organization’s users, devices, applications, data, budget, and risk level.

Before selecting a platform, consider:

  • How many endpoints need protection?
  • Which operating systems are being used?
  • Do employees work remotely?
  • Does the business require EDR capabilities?
  • How quickly can the organization respond to security alerts?
  • Is centralized management required?
  • Does the business need automated threat response?
  • Are ransomware and phishing major concerns?
  • What reporting and compliance requirements exist?
  • Can the solution scale as the business grows?

A solution should provide practical protection without creating unnecessary complexity for the IT team.

Building a Layered Cybersecurity Strategy

Endpoint protection should not operate as the only security control in a business. Instead, endpoint protection should work as one part of a coordinated cybersecurity architecture.

A stronger security environment combines endpoint security with other layers such as:

  • Firewall protection
  • Email security
  • Multi-factor authentication
  • Secure Wi-Fi
  • Network monitoring
  • Regular software updates
  • Data backup
  • Employee security awareness
  • Access controls
  • Incident response planning

For example, an email security system may block a suspicious message before an employee opens it, while endpoint security can provide another layer if a malicious file reaches the device.

Similarly, reliable backups can help an organization recover important information if ransomware or another destructive incident occurs.

Common Mistakes SMEs Make

Business leaders often think of cybersecurity in the same terms as a fire alarm – a thing that gets ‘installed.’ This is a misunderstanding. Security threats evolve constantly, so businesses need to keep adapting their policies, updating procedures, and revising their response plans accordingly.

Another mistake is providing security for the desktop only and ignoring laptops and remote employees.

Finally, it is a mistake to assume that a security product solves all cybersecurity issues. Employees must be security educated, access must be monitored, software must be current, and data must be backed up.

Ignoring security alerts is also a mistake. If you are getting repeated alerts, that is a sign that something needs to be investigated.

Benefits of Professional Endpoint Security Management

As an SME expands, management of endpoint security across multiple devices becomes cumbersome. With professional endpoint security management, businesses can implement the right policies and stay on top of alerts and incidents as they come up. 

Managed endpoint security services become essential for businesses without an in-house cybersecurity team.

Endpoint security management offers a host of advantages to businesses including the deployment and configuration of endpoint security solutions, proactive security and management of endpoint security solutions, and reporting and endpoint security health status reviews.

This allows employees to concentrate on managing the business, while professional security management services take care of security management.

How Endpoint Protection Supports Business Continuity

How Endpoint Protection Supports Business Continuity

There is a close relationship between business continuity and cybersecurity. A compromised endpoint results in disruption of business operations, downtime, and increased unplanned cost of business recovery.

Endpoint protection solutions are designed to reduce the likelihood and impact of device-based security threats. 

These security solutions should be integrated with resilient business operations, backup services, recovery services, and an articulated incident response security management service.

The goal is not just to prevent endpoint security incidents, but to ensure business continuity.

Final Thoughts

For small and medium businesses, endpoint device security is a necessity. Security of devices that transmit business sensitive information and connect employees to cloud services is of paramount concern.

This kind of strategy helps businesses prevent ransomware and malware attacks, and improves the response and visibility of protective security layers across the devices.

The best endpoint protection approach is the integration of endpoint security, comprehensive network security protection, backup security services, employee security awareness services, and professional security oversight.

For SMEs in the UAE, particularly businesses that have presence in Dubai, Abu Dhabi, and Sharjah, a security strategy that is practical and that considers the actual devices, users, applications, and risk profile of the organization ought to be most appropriate.

Frequently Asked Questions

Yes. Small businesses can face malware, ransomware, phishing, and credential attacks just like larger organizations. The right security controls can help reduce these risks.

Not exactly. Antivirus is generally one component of a broader endpoint security strategy. Modern solutions can add behavioral monitoring, centralized management, detection, investigation, and response.

Yes. Many modern platforms can protect and manage devices outside the office, making them useful for remote and hybrid work environments.

Yes. A firewall protects your network perimeter. Endpoint protection protects the individual devices — which matters a lot once employees work remotely or use personal devices that sit outside that perimeter.

It depends on your existing setup and priorities — whether you value fastest detection, easiest management, or built-in backup/recovery. Talking to a provider who can assess your current environment is usually faster than comparing spec sheets alone.

It can help detect and block many ransomware behaviors, but no single security product can guarantee complete protection. Businesses should also maintain secure, tested backups and other security controls.